


Free May-2026 SC-900 Dumps are Available for Instant Access
View All SC-900 Actual Exam Questions Answers and Explanations for Free
NEW QUESTION # 10
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/overview-identity-protection https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks https://docs.microsoft.com/en-us/azure/active-directory/authentication/tutorial-risk-based-sspr-mfa
NEW QUESTION # 11
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 12
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
A screenshot of a computer Description automatically generated with low confidence
You can use an Azure network security group to filter network traffic to and from Azure resources in an Azure virtual network. A network security group contains security rules that allow or deny inbound network traffic to, or outbound network traffic from, several types of Azure resources. For each rule, you can specify source and destination, port, and protocol.
NEW QUESTION # 13
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:

NEW QUESTION # 14
Select the answer that correctly completes the sentence.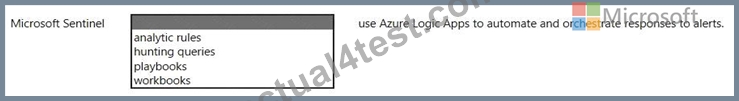
Answer:
Explanation:
Explanation
playbooks
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
NEW QUESTION # 15
Which Microsoft 365 feature can you use to restrict communication and the sharing of information between members of two departments at your organization?
- A. Customer Lockbox
- B. Privileged Access Management (PAM)
- C. information batteries
- D. sensitivity label policies
Answer: C
NEW QUESTION # 16
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: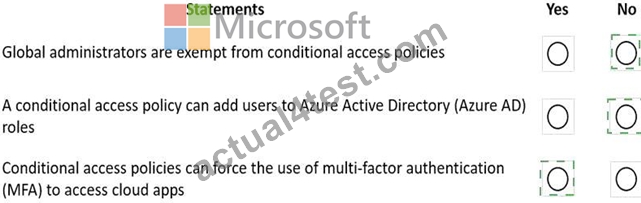
Explanation:
Microsoft explains that Conditional Access (CA) evaluates signals and then enforces access decisions using grant and session controls: "Conditional Access policies are enforced after first-factor authentication is completed" and are used to "make access control decisions." CA policies target users and groups-including administrators-unless explicitly excluded. Microsoft guidance recommends excluding only break-glass accounts: "Customers with Azure AD roles such as Global administrator should have at least one emergency access account excluded from policies." This means admins are not exempt by default; they are in scope unless you configure exclusions.
CA does not manage directory role assignments; that is handled by role assignment and Privileged Identity Management (PIM). CA's grant controls focus on access conditions: "Grant access... Require multi-factor authentication" and Microsoft lists a common baseline: "Require multi-factor authentication for all users." Therefore, CA can require MFA to access cloud apps, but it cannot add users to Azure AD roles.
These statements from Microsoft's SCI materials confirm the outcomes: Admins are not inherently exempt (No), CA cannot assign roles (No), and CA can force MFA for app access (Yes).
NEW QUESTION # 17
For each of the following statements, select Yes if the statement is true Otherwise, select No.
NOTE Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 18
Select the answer that correctly completes the sentence.
Answer:
Explanation:

NEW QUESTION # 19
What can you use to ensure that all the users in a specific group must use multi-factor authentication (MFA) to sign in to Azure AD?
- A. a communication compliance policy
- B. a user risk policy
- C. a Conditional Access policy
- D. Azure Policy
Answer: C
Explanation:
According to Microsoft's Security, Compliance, and Identity (SCI) documentation and learning paths (specifically SC-900, SC-300, and Azure AD Identity Protection modules):
"Conditional Access policies in Azure AD are the primary method for enforcing access controls based on specific conditions such as user, group, location, device compliance, and application." In this case, the organization can configure a Conditional Access policy that targets a specific Azure AD group and requires MFA as a condition before access is granted. The typical policy setup includes:
* Assignments: Target users or groups (e.g., "Finance Department Users").
* Cloud apps or actions: Specify which applications or services are protected (e.g., Microsoft 365).
* Access controls: Set the control to "Require multi-factor authentication." Microsoft's SCI training materials further state:
"Conditional Access enables administrators to enforce MFA for specific users, groups, or scenarios. It provides flexibility to protect access without enabling MFA globally for all users." Other options explained:
* Azure Policy (A) applies to Azure resources, not user authentication.
* Communication compliance policy (B) monitors message content for compliance violations.
* User risk policy (D) is part of Azure AD Identity Protection, enforcing MFA based on detected user risk levels, not group membership.
Therefore, the verified and correct answer is: # C. a Conditional Access policy.
NEW QUESTION # 20
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
NEW QUESTION # 21
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/overview
NEW QUESTION # 22
Which two Azure resources can a network security group (NSG) be associated with? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A. a virtual network
- B. an Azure App Service web app
- C. a virtual network subnet
- D. a network interface
- E. a resource group
Answer: C,D
Explanation:
You can use an Azure network security group to filter network traffic to and from Azure resources in an Azure virtual network. A network security group contains security rules that allow or deny inbound network traffic to, or outbound network traffic from, several types of Azure resources.
NEW QUESTION # 23
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
NEW QUESTION # 24
Which service should you use to view your Azure secure score? To answer, select the appropriate service in the answer area.
Answer:
Explanation:
Explanation
Security Center
NEW QUESTION # 25
Select the answer that correctly completes the sentence.
Answer:
Explanation:
Explanation:
Graphical user interface, text, application Description automatically generated
NEW QUESTION # 26
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated
NEW QUESTION # 27
Select the answer that correctly completes the sentence.
Answer:
Explanation:
NEW QUESTION # 28
Which service should you use to view your Azure secure score? To answer, select the appropriate service in the answer area.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/secure-score-access-and-track
NEW QUESTION # 29
Match the Microsoft 365 insider risk management workflow step to the appropriate task.
To answer, drag the appropriate step from the column on the left to its task on the right. Each step may be used once, more than once, or not at all.
NOTE: Each correct match is worth one point.
Answer:
Explanation:

NEW QUESTION # 30
......
The Most In-Demand SC-900 Pass Guaranteed Quiz : https://www.actual4test.com/SC-900_examcollection.html
New Version SC-900 Certificate & Helpful Exam Dumps is Online: https://drive.google.com/open?id=1s9T5267uyLWqOpbBRHoKQzpFlkEZ_OuF